Master threat detection, SIEM analytics, and cloud defense with deep foundational training and specialized digital assets. 15 core curriculum modules available now, with scenario-based practical labs rolling out as part of your training journey.
15
Core Modules
180
12 Assets / Module
$15
Card / International
Rs 1,000
EasyPaisa / JazzCash
Preview how CyberAura breaks down high-level network architecture, TCP/IP vs OSI layers, port mechanics, and how adversaries exploit unmonitored communication layers.
Lecture Chapters & Timestamps:
1 Master Video + 1 Audio + 5 PDFs + 5 Videos
Includes comprehensive protocol maps, TCP/UDP packet dictionaries, and architecture breakdown slides.
Unlock All 15 Modules ($15 / PKR 1,000)The complete masterclass package engineered for defenders, security engineers, and researchers. Across 15 core disciplines, every single module delivers exactly 12 structured digital assets for complete mastery.
Precisely 12 structured assets in every module (15 × 12 = 180 Assets)
Comprehensive, structured presentation breaking down the entire domain.
High-fidelity audio edition for commuting, review, and spaced repetition.
Downloadable reference slides, protocol summaries, and syntax cheat sheets.
Targeted visual walkthroughs explaining specific schematics and attack paths.
15 Modules × 12 Assets = 180 total downloadable learning resources.
Scenario-based hands-on practical labs are currently in active production. Enrolling in the launch package grants you 100% free lifetime access to all future lab environments when they deploy.
15 Core Modules + 180 Downloadable Assets
Standard flat fee for international buyers via Card (Visa, MasterCard).
Pakistan EasyPaisa & JazzCash Support:
Pay PKR 1,000 directly via EasyPaisa, JazzCash, or Pakistani local banking on our official store or checkout link.
Everything Included in the Vault:
15 deep-dive technical domains engineered for complete conceptual and tactical mastery. Each module delivers 1 Master Video, 1 Master Audio, 5 PDF Guides, and 5 Explainer Videos (12 assets each).
Dissection of OSI and TCP/IP models, port dynamics (22, 80, 443, 25), TCP 3-way handshakes, UDP routing, ARP spoofing mechanics, and packet stream forensics.
Linux security architecture, kernel namespaces, permissions models (SUID/SGID), /proc file system introspection, systemd services, and incident triage.
Public Key Infrastructure, symmetric vs asymmetric ciphers, hashing algorithms (SHA-256, bcrypt), digital signatures, TLS handshakes, and certificate authorities.
SIEM architectural patterns, log ingestion pipelines, alert triaging lifecycles, correlation logic, false-positive reduction, and tier 1-3 analyst operations.
Shared responsibility model, multi-tenant boundaries, AWS and Azure security baselines, CloudTrail audit structures, and serverless isolation principles.
Evidence preservation, order of volatility, disk imaging forensics, forensic timeline reconstruction, chain of custody protocols, and containment runbooks.
Vulnerability assessment frameworks, CVSS 3.1 scoring formulas, threat modeling matrices, attack surface mapping, and penetration testing methodologies.
OWASP Top 10 core concepts, SQL injection anatomy, Cross-Site Scripting (XSS), CSRF tokens, secure session management, and HTTP defense headers.
Static vs dynamic analysis fundamentals, PE file structures, packing identification, disassembly fundamentals, and safe sandbox inspection architectures.
Tactical, operational, and strategic CTI; Diamond Model of Intrusion; Pyramid of Pain; STIX/TAXII feed standards; and adversarial attribution frameworks.
Zero trust enterprise identity, RBAC vs ABAC models, SAML 2.0 & OAuth2 / OpenID Connect federation, privilege creep prevention, and Active Directory security.
Shift-left philosophy, automated SAST and DAST integration points, container vulnerability scanning, secrets management vaults, and pipeline integrity.
Endpoint detection mechanics, behavioral heuristics, LOLBAS (Living Off the Land) techniques, kernel hooks, telemetry collectors, and automated containment.
SCADA and industrial control architectures, the Purdue Enterprise Reference Grid, Modbus and DNP3 protocol vulnerabilities, and critical infrastructure defense.
Principles of cyber deception, dynamic honey-tokens, canary files, honeypot network placement, legal boundaries, and adversary friction economics.
Hands-on technical lab environments and scenario-based simulation ranges are currently being built to complement each theoretical discipline. All students who enroll now receive these practical lab environments as a complimentary free update upon launch.
Live Wazuh and Elastic environment configured to parse real adversarial telemetry. Write custom alert rules and triage simulated multi-stage attacks.
Hands-on domain controller virtual range. Detect Kerberoasting requests, monitor SPN enumeration, and configure decoy service accounts.
Simulated cloud breach scenario. Audit unauthorized privilege escalation, trace S3 bucket exposure, and isolate compromised EC2 instances.
Hands-on Wireshark and Zeek packet analysis on raw malicious captures. Uncover hidden DNS exfiltration channels and encrypted beaconing patterns.
Deploy dynamic honeytokens, fake database tables, and tripwired credentials that notify webhooks instantaneously upon attacker interaction.
Comprehensive defender challenge: trace the attack lifecycle from initial perimeter breach to root cause containment and executive debrief.
When you purchase the CyberAura Mega-Bundle for $15 (or PKR 1,000 in Pakistan), all upcoming practical labs, virtual range files, and walkthroughs will be credited directly to your account with zero added charges.
Participate in specialized live webinars, technical breakdowns, and interactive Q&A sessions led by instructor Touheed Ahmed and guest defensive architects.
Step-by-step breakdown tracing how an attacker traverses from initial unmonitored port exposure to domain escalation, and how modern SIEMs correlate the forensic trail.
Practical demonstration on generating believable canary credentials, fake database tables, and tripwire files that alert SOC analysts before data exfiltration occurs.
Open discussion with Touheed Ahmed on essential conceptual competencies, port mastery, interview frameworks, and building credibility as an aspiring analyst.
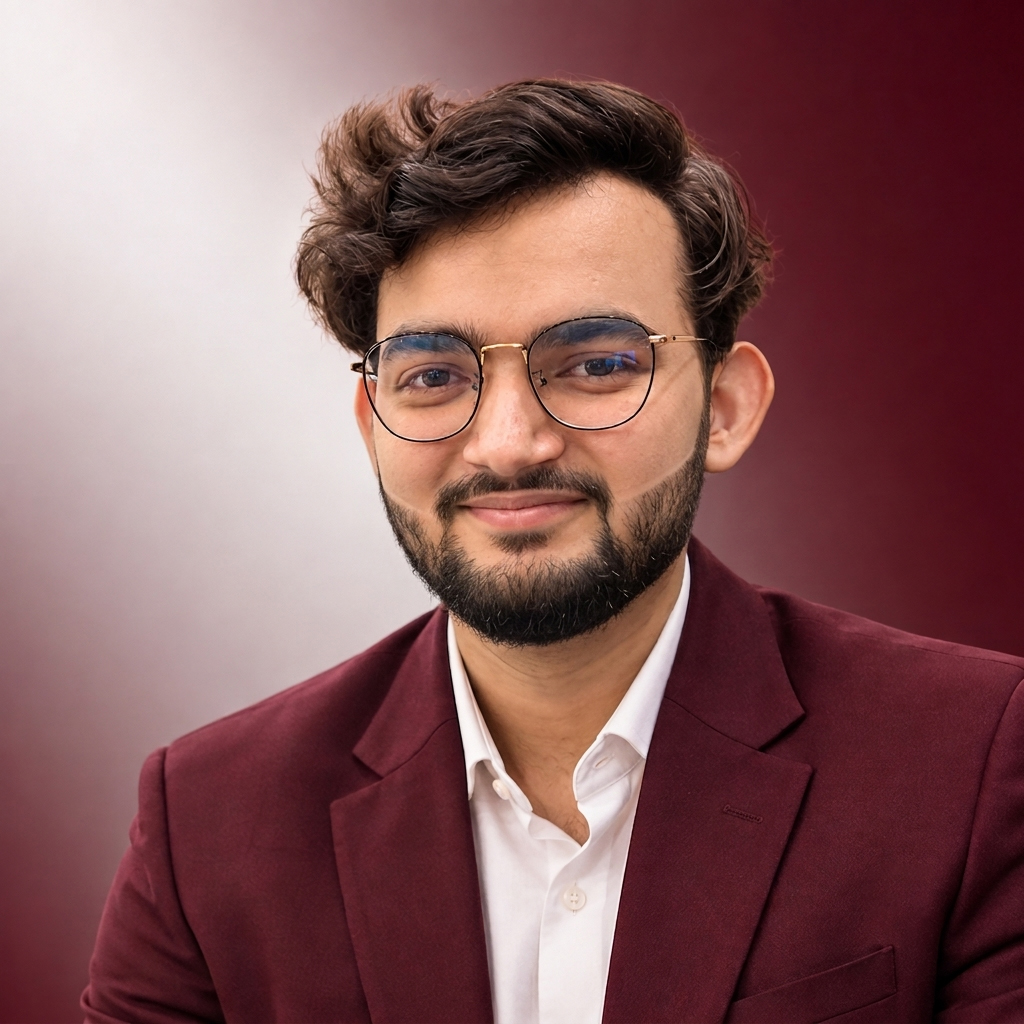
CyberAura Founder
Founder & Lead Security Architect
Network Security · Digital Forensics · Active Cloud Defense
At CyberAura, our mission is to build rock-solid foundational security engineering skills for aspiring defenders and seasoned security practitioners alike. Founded by Touheed Ahmed, CyberAura delivers an uncompromising curriculum covering network packet behavior, cloud posture, and forensic investigation.
Specializing in Network Security, Digital Forensics, and Active Cloud Defense, Touheed structured the 180-Asset Cybersecurity Mega-Bundle so every learner masters the intricate architectural blueprints, communication flows, and threat models before stepping into live adversary combat.